

When you’re finished with this course, you’ll have the talents and information of assaults on cryptographic applications and protocols needed to implement stronger cryptographic protocols to secure data. In order to achieve it, they maintained secrecy about encryption algorithms and encryption machine devices and completely tested the reliability of personnel who had access to cryptosystems. Nonetheless, already within the XIX century, consultants in the field of cryptography instructed that the secrecy of encryption algorithms isn’t a assure towards hacking (Lou et al., 2021). Furthermore, it was realized that a truly reliable encryption system ought to remain safe even when an opponent fully recognizes the cryptographic algorithm. Storage, transmission, and transformation of knowledge are subjected to various attacks.
Utility & Api Security
They mannequin sensible scenarios where attackers work together with cryptographic techniques rather than just observing them. Encrypting sensitive assets corresponding to databases, storage volumes, and backups must be a default operation managed by automation, not guide processes. Safety teams should leverage tools that provide real-time monitoring, alerting, and self-healing for cryptographic controls so that deviations from coverage or finest practices trigger immediate responses. Common rotation and timely destruction of old or probably uncovered keys cut back threat and contain the influence of key compromise.
Why Radware? Find Out How Our Ai-powered Platform Quickly Resolves Points
- Avoid legacy alternatives or permitting insecure downgrades, as these create clear paths for visitors interception or lively manipulation.
- In an MITM attack, a hacker intercepts and probably alters communication between two events.
- Regular rotation and well timed destruction of old or probably uncovered keys scale back danger and include the influence of key compromise.
- Otherwise, it’s affordable to imagine that the adversary knows every thing about the encryption system in use besides the applicable keys when assessing encryption safety.
Cryptographic failures are vulnerabilities that occur when applications poorly implement or use cryptography, leading to the publicity of sensitive data. The document outlines various cryptographic assaults, including passive and lively attacks, cryptographic attacks, and software-based assaults, emphasizing the importance of understanding these types for secure system design. It additionally covers encryption methods such as Hill Cipher and Playfair, the Euclidean algorithm for GCD calculation, and details on the Knowledge Encryption Commonplace (DES) and its rounds. Moreover, it discusses block cipher modes, SHA-512 hashing, message authentication codes, public key distribution strategies, X.509 certificates fields, and the Kerberos authentication protocol. Modern digital methods rely on cryptography to make sure safe communication—but vulnerabilities in implementation can open the door to severe attacks. In this course, Cryptographic Purposes and Attacks, you’ll be taught assaults against cryptographic protocols and purposes.
Automation is essential to making sure consistent, error-free cryptography throughout complex environments. Configuration-as-code, automated coverage enforcement, and steady scanning for misconfigurations help establish and remediate weaknesses earlier than they can be exploited. Integrating cryptographic well being checks into CI/CD pipelines can catch unintentional regressions or non-compliance issues early within the software improvement lifecycle.
Network Security Ideas
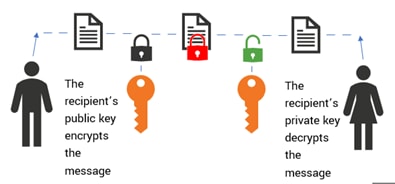
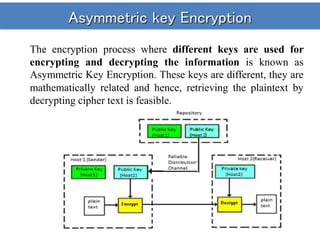
Repository containing my Sage and/or Python implementations of attacks on in style ciphers and public key cryptosystems. Cryptography includes techniques https://logotype.dev/articles/understanding-logo-software-how-it-transforms-your-branding-experience for secure communication, making certain that solely the sender and intended recipient can perceive the transmitted info. It has keys for encryption (transforming plaintext into unreadable ciphertext) and decryption (reverting ciphertext again to readable form).
Insecure Database Encryption Workflows
Periodic critiques by unbiased specialists or penetration testers who concentrate on cryptographic methods provide an exterior perspective and infrequently catch points missed by inner groups. Committing to a schedule of periodic evaluate retains cryptographic controls current and tuned to the evolving risk panorama. Incorrect use of APIs, misunderstanding threat fashions, skipping vital steps like verification of cryptographic parameters, or custom-building cryptographic modules with out deep expertise create numerous failure points. This additionally includes logic flaws similar to misuse of encryption modes, hardcoded IVs (initialization vectors), or insecure random quantity generation.
